BLOG / TECHNICAL LIBRARY 285
What Evidence Should Precede an RF Security Decision?
A project-level guide to using authorised RF reception as one governed input in security decision-making. It focuses on evidence ownership, protected services, privacy, lawful spectrum use, safe offsets, accountable human review, and written validation—without prescribing operational sensing or response techniques.
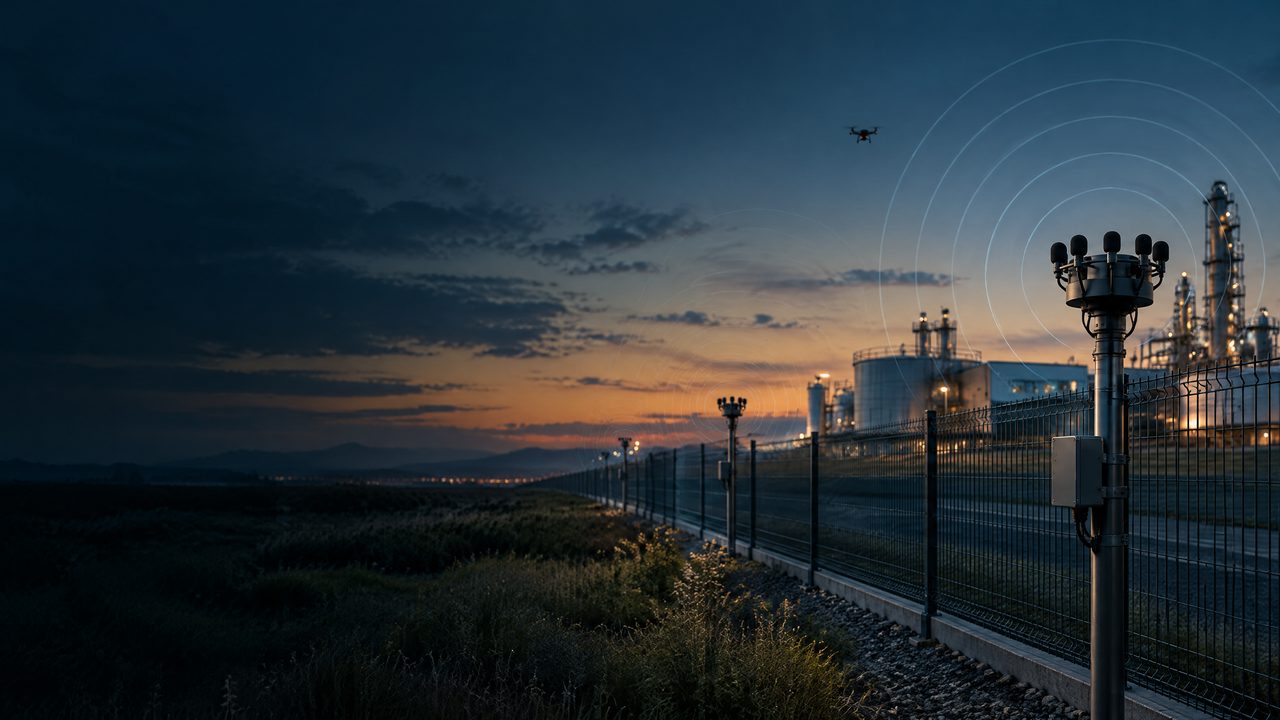
INFORMATION & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put technology questions back into an authorised, reviewable, and verifiable project context.
This conceptual scene helps explain conditional information, protected services, human review, and written validation. It is not a deployment or field-outcome claim.
BLOG SUMMARY
The decision is the product
RF-related information can be useful only when its meaning, limits, and consequences are made explicit. This guide frames identification as an accountable evidence question: what was authorised, what was observed, what remains uncertain, who reviews it, and what record supports the next proportionate decision. The aim is a defensible process rather than a promise of detection, classification, tracking, coverage, or site suitability.
TERMS IN THIS GUIDE
Hover, focus, or tap a term for a bounded definition. Each definition links to the terminology reference.
PROJECT QUESTION / 01
1. Start with the decision boundary, not a device brief
Before any discussion of an RF input, the project should state which security decision needs support, which protected services must remain available, and which actions are outside scope. That boundary should identify the accountable owner, applicable privacy expectations, lawful spectrum-use obligations, EMC and permit review, and the conditions under which information may be retained or shared. Framing the question this way prevents a technical component from silently becoming an authority to act, and it gives reviewers a common standard for relevance, proportionality, and escalation.
CONTEXT & UNCERTAINTY / 02
2. Treat RF reception as contextual evidence
Authorised RF reception should be described as a source of information whose interpretation depends on context, governance, and documented uncertainty—not as an automatic identity or verdict. A project record can distinguish an observation from an inference, record the time and provenance of material, and note protected communications, privacy boundaries, and lawful-use constraints. If other approved information sources are considered, multi-sensor corroboration should mean disciplined comparison of evidence and disagreement, not an assumption that combined inputs are inherently accurate or complete.
PROTECTION & COMPLIANCE / 03
3. Build safe offsets and human review into the workflow
A responsible plan makes room between an ambiguous observation and a consequential security decision. Safe offsets can include time for a qualified reviewer, separation between analytical notes and operational authority, privacy-preserving handling, and a clear route for challenge or correction. Human review should test alternative explanations, examine uncertainty and missing context, and confirm that any proposed decision is proportionate to the evidence and the protected service at stake. No automated label should remove that accountability or imply that a response is warranted.
GOVERNANCE & VALIDATION / 04
4. Close the loop with written validation
Written validation is the project’s durable test of whether the governance question was answered, not a performance certificate for a sensor or site. It should capture the authorised purpose, assumptions, exclusions, review roles, evidence-handling rules, EMC and permit status, safe-offset decisions, known uncertainties, and unresolved questions. Stakeholders can then approve, revise, or reject a use case on an auditable basis. Validation should remain bounded to the stated project question and should never be read as a guarantee of accuracy, coverage, identification, or outcomes.
TECHNICAL & COMPLIANCE BOUNDARY / 05
This guide is an educational project reference—not an operating, deployment, integration, or performance instruction.
01Availability and interpretation of acoustic, RF, radar, EO/IR, visual, and other information depend on site conditions, environment, data quality, protected services, permissions, privacy, and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, availability, safety, non-interference, or risk outcomes.
02Any equipment, interface, data handling, industrial-system connection, spectrum-related arrangement, aviation coordination, or later project decision requires appropriate authority, engineering review, qualified personnel, and written scope.
03The public guide does not provide target selection, sensor positioning, thresholds, algorithms, execution sequences, signal control, interference, navigation manipulation, or response methods.
BLOG FAQ / 285
Frequently asked questions on What Evidence Should Precede an RF Security Decision?.
These answers support bounded, project-level discussion. They are not an operating, deployment, integration, or field-outcome instruction.
RECORDTECHNICAL LIBRARY / GOVERNED INFORMATION FAQ
NEXT STEP / PROJECT PATH
Discuss PCBA delivery and custom-project conditions.
From sensing modules to system integration, interfaces, environmental fit, certification, and documentation scope belong in a written project definition.
CONTINUE THE READING
CONTENT DISTRIBUTION / SHARE
Share this reviewed project release.
Opens the platform share interface in a new window.
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
Acoustic Drone Detection vs. RF Detection: Why Critical Infrastructure Needs Multiple Sensors
A governance-first comparison of passive acoustic and RF information roles for airports, energy facilities, ports, data centres and other critical infrastructure. It explains conditional evidence, protected services, accountable review, lawful authority, integration and written validation—not a sensor prescription, placement plan, threshold, signal-control method or performance claim.
Drone Detection for Critical Infrastructure: A Project Guide for Airports, Energy Facilities and Data Centers
A governance-first guide to discussing acoustic, RF, radar, EO/IR and visual information for airports, energy facilities, ports and data centres. It frames protected services, conditional evidence, interfaces and written validation—not a sensor prescription, deployment plan, threshold, control method or performance claim.