BLOG / TECHNICAL LIBRARY 383
RF Detection Architecture: Governance at Network Scale
Large security networks make RF drone detection an architecture and governance question, not a promise of continuous awareness. This guide focuses on a project decision: how to define evidence boundaries, authorised data flows, human review, privacy safeguards, and lifecycle records before a multi-site design is assessed. It keeps analytic context separate from response operations and treats lawful permissions, EMC, and protected services as design inputs.
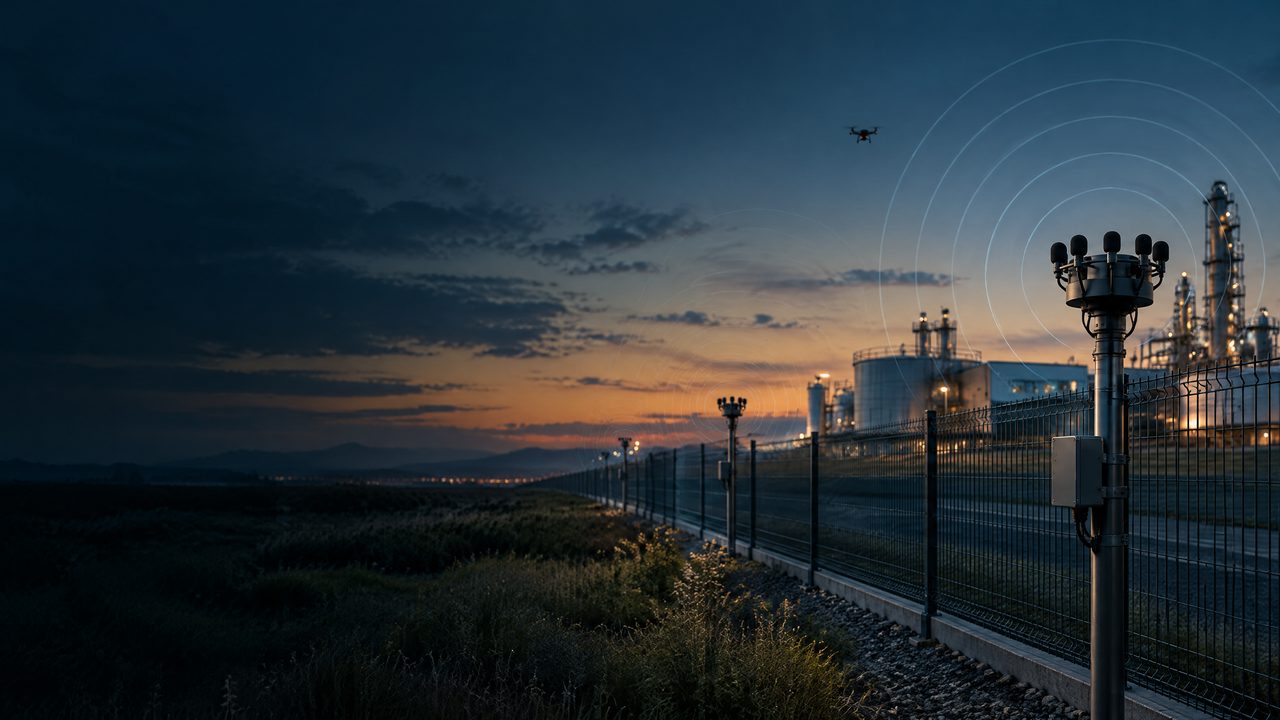
INFORMATION & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put technology questions back into an authorised, reviewable, and verifiable project context.
This conceptual scene helps explain conditional information, protected services, human review, and written validation. It is not a deployment or field-outcome claim.
BLOG SUMMARY
Start with an Evidence Boundary
Large security networks make RF drone detection an architecture and governance question, not a promise of continuous awareness. This guide focuses on a project decision: how to define evidence boundaries, authorised data flows, human review, privacy safeguards, and lifecycle records before a multi-site design is assessed. It keeps analytic context separate from response operations and treats lawful permissions, EMC, and protected services as design inputs.
TERMS IN THIS GUIDE
Hover, focus, or tap a term for a bounded definition. Each definition links to the terminology reference.
PROJECT QUESTION / 01
Start with an Evidence Boundary
The first architecture decision is what the project can legitimately claim. Define RF analytics as an information service with a documented evidence boundary, rather than as a guaranteed detector. Record which authorised information inputs may be considered, what uncertainty remains, and which conclusions require human review. Separate observation, correlation, and assessment in project language; avoid presenting an analytic indication as identity, intent, or confirmation. A requirements register should link each proposed use to a responsible owner, lawful purpose, retention decision, and written acceptance condition. This framing helps security, legal, privacy, and engineering stakeholders challenge assumptions early, while keeping the public description educational and independent of any vendor or site-specific outcome.
CONTEXT & UNCERTAINTY / 02
Govern the Multi-Site Information Flow
At network scale, interfaces and accountability matter as much as analytic design. Describe information movement by role and purpose, not by exposed endpoints or implementation credentials. The architecture record should identify approved interfaces, data minimisation rules, access responsibilities, audit ownership, and conditions for sharing indications between locations. Establish how time, provenance, versioning, and uncertainty are represented so reviewers can understand context without treating a common format as proof. Protected services and other spectrum users should be considered through documented coordination and authorised information inputs. Any integration should pass a written interface review covering privacy, security, change control, and failure handling before it becomes part of an operationally relevant workflow.
PROTECTION & COMPLIANCE / 03
Make Human Review and Privacy Explicit
A network-wide analytic picture still needs accountable interpretation. Specify where trained, authorised people review analytic context and how disagreement, ambiguity, or missing evidence is recorded. Human review should not be reduced to a button press or an automatic escalation rule; it is a governance control that preserves proportionality and traceability. Privacy documentation should state the lawful basis, minimisation approach, retention limits, access review, and process for correcting an inaccurate record. Consider bystanders, adjacent organisations, and sensitive locations when defining collection and reporting boundaries. Public materials should explain these safeguards without revealing sensitive site details, personal data, interface credentials, or operational response procedures.
GOVERNANCE & VALIDATION / 04
Validate Through Lifecycle Records
Architecture is credible only when its assumptions can be revisited. Use a staged validation record that connects the approved scope to EMC assessment, lawful permissions, safe offsets, protected-service considerations, interface governance, and documented limitations. Written validation should test whether information is handled as intended in representative, authorised conditions; it should not be presented as a universal performance guarantee. Maintain change records for software, data sources, sites, responsibilities, and retention rules, with an owner for re-approval. Periodic review should ask whether the original evidence boundary still fits the mission, community expectations, and regulatory context. Retirement and archival decisions belong in the same lifecycle plan.
TECHNICAL & COMPLIANCE BOUNDARY / 05
This guide is an educational project reference—not an operating, deployment, integration, or performance instruction.
01Availability and interpretation of acoustic, RF, radar, EO/IR, visual, and other information depend on site conditions, environment, data quality, protected services, permissions, privacy, and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, availability, safety, non-interference, or risk outcomes.
02Any equipment, interface, data handling, industrial-system connection, spectrum-related arrangement, aviation coordination, or later project decision requires appropriate authority, engineering review, qualified personnel, and written scope.
03The public guide does not provide target selection, sensor positioning, thresholds, algorithms, execution sequences, signal control, interference, navigation manipulation, or response methods.
BLOG FAQ / 383
Frequently asked questions on RF Detection Architecture: Governance at Network Scale.
These answers support bounded, project-level discussion. They are not an operating, deployment, integration, or field-outcome instruction.
RECORDTECHNICAL LIBRARY / GOVERNED INFORMATION FAQ
NEXT STEP / PROJECT PATH
Discuss PCBA delivery and custom-project conditions.
From sensing modules to system integration, interfaces, environmental fit, certification, and documentation scope belong in a written project definition.
CONTINUE THE READING
CONTENT DISTRIBUTION / SHARE
Share this reviewed project release.
Opens the platform share interface in a new window.
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
Acoustic Drone Detection vs. RF Detection: Why Critical Infrastructure Needs Multiple Sensors
A governance-first comparison of passive acoustic and RF information roles for airports, energy facilities, ports, data centres and other critical infrastructure. It explains conditional evidence, protected services, accountable review, lawful authority, integration and written validation—not a sensor prescription, placement plan, threshold, signal-control method or performance claim.
Drone Detection for Critical Infrastructure: A Project Guide for Airports, Energy Facilities and Data Centers
A governance-first guide to discussing acoustic, RF, radar, EO/IR and visual information for airports, energy facilities, ports and data centres. It frames protected services, conditional evidence, interfaces and written validation—not a sensor prescription, deployment plan, threshold, control method or performance claim.