BLOG / TECHNICAL LIBRARY 520
Multi-Sensor C-UAS Information Governance for Critical Infrastructure
An educational guide to governing information in critical-infrastructure C-UAS projects. It explains how multiple inputs may have separate, bounded evidence roles under lawful authority, data and interface governance, human review, written acceptance and controlled change. It is not an operating method, a sensor design, a selection method, a response instruction or a claim that any combination will detect, identify, perform, remain available or make a site safe.
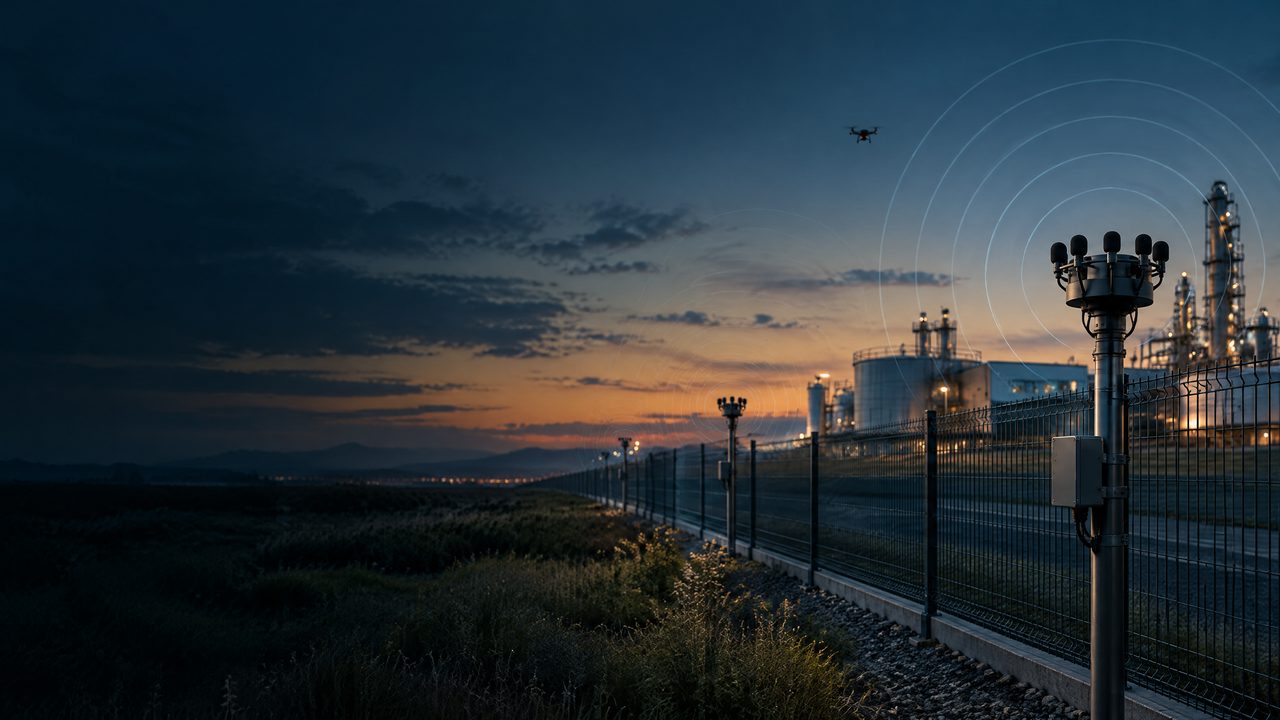
INFORMATION, EVIDENCE & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put C-UAS project questions into an authorised, reviewable and verifiable governance context.
This conceptual scene explains protected services, conditional evidence, human review and written acceptance. It is not a deployment or field-outcome claim.
BLOG SUMMARY
Multiple inputs do not remove uncertainty; governance makes their limits reviewable
A critical-infrastructure project may receive information from several sources, legacy systems and partner-managed services. The governance task is not to merge those inputs into an unqualified conclusion. It is to define the protected service, establish authority, distinguish evidence roles, document provenance and quality limits, assign data and interface accountability, and keep uncertainty available to authorised reviewers. A written baseline, acceptance record and change-control process ensure that additions or alterations are assessed rather than silently changing the project’s claimed purpose.
PROJECT CONTEXT / 01
1. Establish governance around the protected service
Begin by recording the critical service, continuity objective, accountable owner, legal and organisational authority, safety and privacy obligations, and the decisions for which information may be reviewed. Different infrastructure environments have different constraints and stakeholders. A generic category label, public incident report or market assertion cannot supply the project’s authority model, acceptance conditions or evidence standard.
EVIDENCE ROLES / 02
2. Assign bounded evidence roles to each information source
Each source should have a documented role, provenance, known limitations, dependencies and conditions for interpretation. Information may agree, conflict or be absent; none of those states should be hidden. The project should avoid treating a combined display as proof of identity, intent, risk, location, priority or an authorised action. Combining inputs can support review, but it does not convert uncertainty into a universal result.
DATA & INTERFACE GOVERNANCE / 03
3. Make data and interface accountability explicit
Data classification, access control, retention, auditability, cybersecurity responsibilities, interface ownership, versioning and uncertainty presentation belong in the governance record. Integration questions should be handled through documented responsibilities and approvals, rather than informal assumptions about compatibility. Where a partner or existing platform is involved, the written record should make boundaries of responsibility visible to all authorised parties.
HUMAN REVIEW / 04
4. Preserve human review and a defensible record
Authorised reviewers need context, provenance and limitations in order to assess information responsibly. The project should record who reviews what, how accountability is handed over, how review is auditable and how unresolved uncertainty is communicated. Information governance supports disciplined judgement; it does not delegate legal authority or operational responsibility to a feed, interface, automated process or supplier narrative.
ACCEPTANCE & CHANGE CONTROL / 05
5. Use written acceptance and change control as lifecycle safeguards
The project baseline should describe protected services, evidence roles, data governance, interface boundaries, reviewer responsibilities, acceptance evidence and change-control ownership. Acceptance should be assessed against that written baseline and kept as an evidence record. New data flows, changed interfaces, revised roles or altered assumptions are governance events requiring documented assessment and approval, not silent extensions of an earlier claim.
EDUCATIONAL & COMPLIANCE BOUNDARY / 06
This English guide is an educational, conceptual and project-governance reference—not an operating, deployment, integration or performance instruction.
01Availability and interpretation of information depend on site conditions, environment, data quality, protected services, authority, privacy, existing systems and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, interoperability, availability, safety, non-interference or risk outcomes.
02Any data handling, system interface, connection to an existing platform, partner arrangement or later project decision requires appropriate authority, engineering and compliance review, qualified personnel and written scope.
03This public guide provides no technical configuration, operating procedure, target handling, signal processing, navigation manipulation or response method. Project discussion belongs within an authorised, reviewable and written governance framework.
BLOG FAQ / 520
Questions on Multi-Sensor C-UAS Information Governance for Critical Infrastructure.
These answers support educational, bounded project discussion. They are not operating, deployment, integration, selection or field-outcome instructions.
RECORDTECHNICAL LIBRARY / GOVERNANCE-FIRST PROJECT FAQ
NEXT STEP / PROJECT PATH
Discuss information and integration project conditions through a written scope.
From evidence roles, data and interface accountability and human review to acceptance records and change control, each element belongs in a written project definition.
CONTINUE THE READING
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
C-UAS Partner Integration: Evidence, Interface and Acceptance Governance
An educational project guide for organisations and partners discussing C-UAS integration without turning a partner relationship into an unsupported assurance. It focuses on protected services, written evidence roles, interface and data accountability, authorised human review, documented acceptance and change control. It does not provide operating, deployment, selection, response or performance instructions, and it makes no promise of detection, interoperability, availability, safety or project outcomes.
Passive Acoustic Drone Detection for Energy Infrastructure: A Governance-First Project Guide
An educational, governance-first guide for discussing the conditional role of passive acoustic information in energy-infrastructure projects. It treats information as bounded evidence for authorised human review, documented data handling, written scope and acceptance—not as an operating plan, a response method, a deployment design or a promise of detection, availability, safety or performance.