BLOG / TECHNICAL LIBRARY 222
What Should an Industrial Acoustic Perimeter Project Prove Before It Proceeds?
For a large industrial facility, an acoustic perimeter should be treated as an authorised assurance project—not as a promise of automatic detection or a technical deployment recipe. The responsible question is whether the proposed concept can be governed, privacy-aware, legally reviewed, and validated in writing for the site’s protected services and operating context.
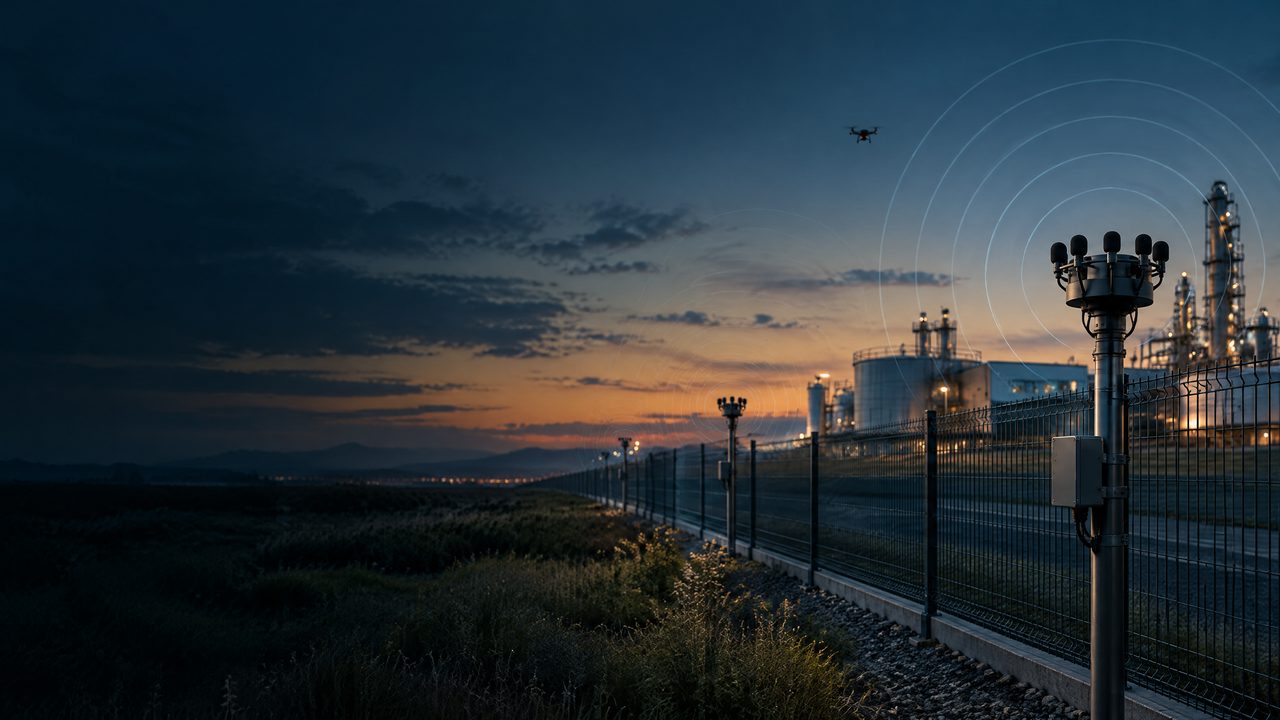
INFORMATION & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put technology questions back into an authorised, reviewable, and verifiable project context.
This conceptual scene helps explain conditional information, protected services, human review, and written validation. It is not a deployment or field-outcome claim.
BLOG SUMMARY
A bounded project question before any technical conclusion
This guide frames acoustic-perimeter planning around project ownership, evidence governance, protected services, safe offsets, human review, privacy, and lawful spectrum use. It is intended to help asset owners, C-UAS providers, and systems integrators define accountable decisions without prescribing sensor placement, operating distances, algorithms, tuning, target selection, or response actions. Any capability statement should remain conditional until an authorised evaluation and written acceptance process has addressed site-specific constraints.
TERMS IN THIS GUIDE
Hover, focus, or tap a term for a bounded definition. Each definition links to the terminology reference.
INFORMATION CONTEXT / 01
1. Define the Protection Question and Accountability
Begin with a written project question: which authorised safety, continuity, or security concern is being examined, and who owns the decision? A facility may have overlapping stakeholders, including operations, security, safety, privacy, legal, and emergency-management teams. A concept of operations can document permitted uses, prohibited interpretations, escalation ownership, and accountable human review without prescribing an operational response flow. For C-UAS contexts, the scope should distinguish an acoustic cue from any later assessment, and should state that no capability, coverage, or outcome is assumed before validation.
CONDITIONS & UNCERTAINTY / 02
2. Govern Evidence, Privacy, and Human Review
Acoustic information can intersect with workers, visitors, neighbours, and ordinary industrial activity. A project brief may therefore set data-minimisation principles, retention and access rules, lawful purpose, notice obligations, and a process for handling contested interpretations. Evidence should be described as context-dependent and subject to authorised human review, not as an unqualified classification. Integrators can propose records for assumptions, exclusions, uncertainty, and audit ownership. Privacy impact review, labour considerations, and jurisdiction-specific requirements should be resolved before any operational claim is accepted.
CORROBORATION / 03
3. Account for Protected Services and Site Constraints
A large facility is an ecosystem of protected services, not an empty acoustic canvas. Production, transport, alarms, communications, maintenance, public access, and neighbouring properties may create obligations or interference concerns. Scoping should identify the services that must remain protected, the authorities able to constrain the project, and safe offsets required by site safety governance. It should also flag EMC, occupational-safety, environmental-noise, planning, spectrum, aviation, and permit questions for qualified review. This approach avoids prescribing geometry or distances while making constraints visible to decision-makers.
GOVERNANCE & VALIDATION / 04
4. Make Validation Written, Bounded, and Reviewable
Before procurement or operational reliance, the parties may agree a written validation plan that defines assumptions, test authority, environmental conditions, privacy safeguards, protected-service checks, acceptance evidence, and limits on interpretation. The plan should record what is not being tested and how uncertainty is reported. It should not promise reliability, identification, suitability, or performance. A staged governance review can require sign-off from the asset owner and relevant legal, safety, privacy, and spectrum authorities before any change in status. Post-review records should preserve traceability without becoming a response manual.
TECHNICAL & COMPLIANCE BOUNDARY / 05
This guide is an educational project reference—not an operating, deployment, integration, or performance instruction.
01Availability and interpretation of acoustic, RF, radar, EO/IR, visual, and other information depend on site conditions, environment, data quality, protected services, permissions, privacy, and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, availability, safety, non-interference, or risk outcomes.
02Any equipment, interface, data handling, industrial-system connection, spectrum-related arrangement, aviation coordination, or later project decision requires appropriate authority, engineering review, qualified personnel, and written scope.
03The public guide does not provide target selection, sensor positioning, thresholds, algorithms, execution sequences, signal control, interference, navigation manipulation, or response methods.
BLOG FAQ / 222
Frequently asked questions on What Should an Industrial Acoustic Perimeter Project Prove Before It Proceeds?.
These answers support bounded, project-level discussion. They are not an operating, deployment, integration, or field-outcome instruction.
RECORDTECHNICAL LIBRARY / GOVERNED INFORMATION FAQ
NEXT STEP / PROJECT PATH
Discuss PCBA delivery and custom-project conditions.
From sensing modules to system integration, interfaces, environmental fit, certification, and documentation scope belong in a written project definition.
CONTINUE THE READING
CONTENT DISTRIBUTION / SHARE
Share this reviewed project release.
Opens the platform share interface in a new window.
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
Acoustic Drone Detection vs. RF Detection: Why Critical Infrastructure Needs Multiple Sensors
A governance-first comparison of passive acoustic and RF information roles for airports, energy facilities, ports, data centres and other critical infrastructure. It explains conditional evidence, protected services, accountable review, lawful authority, integration and written validation—not a sensor prescription, placement plan, threshold, signal-control method or performance claim.
Drone Detection for Critical Infrastructure: A Project Guide for Airports, Energy Facilities and Data Centers
A governance-first guide to discussing acoustic, RF, radar, EO/IR and visual information for airports, energy facilities, ports and data centres. It frames protected services, conditional evidence, interfaces and written validation—not a sensor prescription, deployment plan, threshold, control method or performance claim.