BLOG / TECHNICAL LIBRARY 246
What Should a C-UAS Provider Govern Before Expanding Its Detection Portfolio?
Expanding a drone-detection portfolio is less a product-count exercise than a governed project question: which customer needs, protected services, evidence, and responsibilities can an authorised integration actually support?
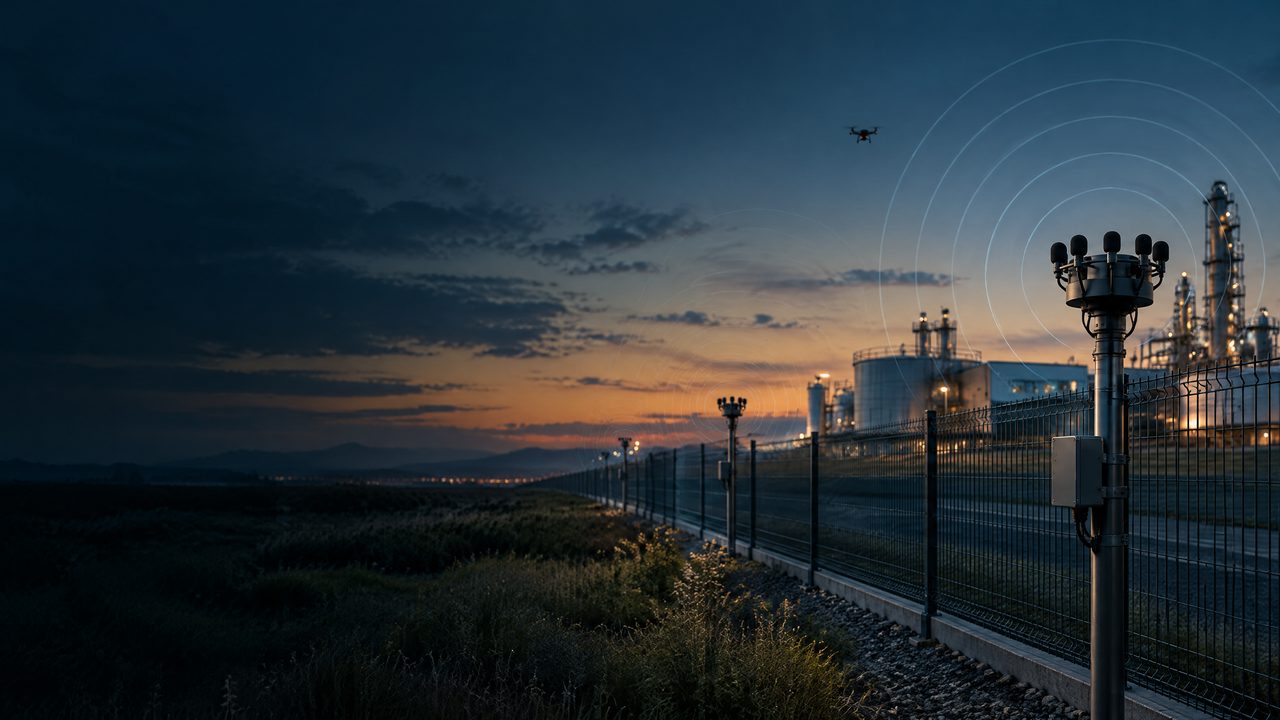
INFORMATION & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put technology questions back into an authorised, reviewable, and verifiable project context.
This conceptual scene helps explain conditional information, protected services, human review, and written validation. It is not a deployment or field-outcome claim.
BLOG SUMMARY
An accountable partnership question before integration
For industrial asset owners, providers, and systems integrators, a disciplined expansion can connect market needs with transparent boundaries. The discussion should centre on authorised scope, written validation, accountable human review, privacy, lawful spectrum use, EMC and permits, safe offsets, and lifecycle ownership—not on placement, geometry, algorithms, operating distances, or performance promises.
TERMS IN THIS GUIDE
Hover, focus, or tap a term for a bounded definition. Each definition links to the terminology reference.
INFORMATION CONTEXT / 01
1. Start with a portfolio-fit question
A provider may begin by mapping customer objectives to decision rights, protected services, and documented use cases. The question is not whether a new sensor can be added, but whether its proposed role is authorised, understandable, and bounded. Industrial owners can state what information they need, who may review it, and which activities remain outside scope. Integrators can then record assumptions, dependencies, privacy considerations, and safe offsets for approval. Any statement about identification, suitability, reliability, or operational value should remain conditional until supported by written, project-specific validation.
CONDITIONS & UNCERTAINTY / 02
2. Make evidence a deliverable, not a slogan
Portfolio expansion is easier to govern when evidence requirements are agreed before commercial language is written. A project team may define what documentation, test context, uncertainty notes, and human-review records are needed to assess a proposed capability. Evidence should distinguish supplier statements from site-specific findings and should identify conditions that could change interpretation. Providers should avoid universal claims about detection, coverage, real-time behaviour, or long-range performance. A written validation plan, accepted by the accountable parties, can set review gates without prescribing sensor placement, algorithms, tuning, or target selection.
CORROBORATION / 03
3. Integrate around accountability and protected services
An OEM or integration partnership should clarify interfaces beyond data exchange. Parties may assign ownership for alert interpretation, access control, records, incident review, maintenance decisions, and escalation to authorised authorities, while keeping accountable human review in the loop. The project should document how aviation, emergency, industrial, and other protected services are considered, and how safe offsets are preserved. No interface specification should be read as permission for signal control, jamming, navigation manipulation, or an operational response flow. Written responsibilities help owners assess governance before accepting a portfolio addition.
GOVERNANCE & VALIDATION / 04
4. Treat compliance and lifecycle as portfolio design
A sustainable expansion includes the full approval and ownership picture. Providers and owners may review privacy obligations, lawful spectrum use, EMC constraints, permits, export or data rules where applicable, cybersecurity expectations, support boundaries, and change control. The commercial package should state what is excluded, what remains subject to local authority, and what must be revalidated after a software, hardware, site, or policy change. This approach does not guarantee an outcome; it creates a traceable basis for procurement, integration, acceptance, renewal, and responsible retirement.
TECHNICAL & COMPLIANCE BOUNDARY / 05
This guide is an educational project reference—not an operating, deployment, integration, or performance instruction.
01Availability and interpretation of acoustic, RF, radar, EO/IR, visual, and other information depend on site conditions, environment, data quality, protected services, permissions, privacy, and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, availability, safety, non-interference, or risk outcomes.
02Any equipment, interface, data handling, industrial-system connection, spectrum-related arrangement, aviation coordination, or later project decision requires appropriate authority, engineering review, qualified personnel, and written scope.
03The public guide does not provide target selection, sensor positioning, thresholds, algorithms, execution sequences, signal control, interference, navigation manipulation, or response methods.
BLOG FAQ / 246
Frequently asked questions on What Should a C-UAS Provider Govern Before Expanding Its Detection Portfolio?.
These answers support bounded, project-level discussion. They are not an operating, deployment, integration, or field-outcome instruction.
RECORDTECHNICAL LIBRARY / GOVERNED INFORMATION FAQ
NEXT STEP / PROJECT PATH
Discuss PCBA delivery and custom-project conditions.
From sensing modules to system integration, interfaces, environmental fit, certification, and documentation scope belong in a written project definition.
CONTINUE THE READING
CONTENT DISTRIBUTION / SHARE
Share this reviewed project release.
Opens the platform share interface in a new window.
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
How C-UAS Integrators Can Turn a Drone Detection Pilot Into a Commercial Project
How C-UAS Integrators Can Turn a Drone Detection Pilot Into a Commercial Project should be discussed as a bounded project question about a governed transition from pilot to commercial project, not as a promise that a technology will detect, identify, locate, track, cover, or protect a particular site. A responsible C-UAS review starts with authority, protected services, privacy, safety, environmental context, accountable human review, and written validation before it treats any sensor indication as decision-ready evidence.
Building a Private-Label UAV Detection Solution for Security Integrators
Building a Private-Label UAV Detection Solution for Security Integrators should be discussed as a bounded project question about private-label security-integrator governance, not as a promise that a technology will detect, identify, locate, track, cover, or protect a particular site. A responsible C-UAS review starts with authority, protected services, privacy, safety, environmental context, accountable human review, and written validation before it treats any sensor indication as decision-ready evidence.