BLOG / TECHNICAL LIBRARY 404
Enterprise UAV Detection: Integrator Project Context
Security integrators working on enterprise and critical-infrastructure projects must design UAV detection as a governed information service, not as an isolated sensor purchase. The central project decision is what evidence the client may lawfully collect, how that evidence will be reviewed, and what records will support later assurance. This guide frames requirements, stakeholder boundaries, privacy, EMC, interfaces, and lifecycle validation without prescribing deployment or operational response.
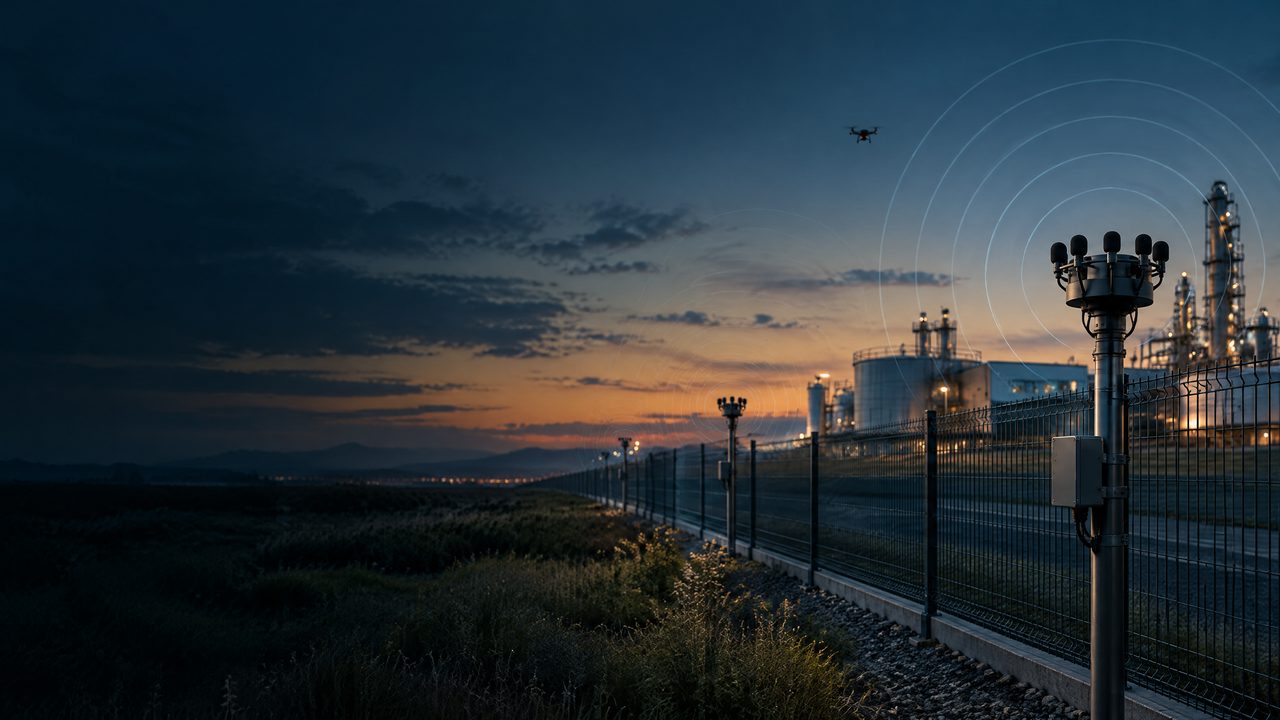
INFORMATION & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put technology questions back into an authorised, reviewable, and verifiable project context.
This conceptual scene helps explain conditional information, protected services, human review, and written validation. It is not a deployment or field-outcome claim.
BLOG SUMMARY
Start with an evidence boundary
Security integrators working on enterprise and critical-infrastructure projects must design UAV detection as a governed information service, not as an isolated sensor purchase. The central project decision is what evidence the client may lawfully collect, how that evidence will be reviewed, and what records will support later assurance. This guide frames requirements, stakeholder boundaries, privacy, EMC, interfaces, and lifecycle validation without prescribing deployment or operational response.
TERMS IN THIS GUIDE
Hover, focus, or tap a term for a bounded definition. Each definition links to the terminology reference.
PROJECT QUESTION / 01
Start with an evidence boundary
Define the information question before discussing equipment. The first design decision is the evidence boundary: what the client needs to know, during which governance-approved phase, and for which documented concern. Integrators should record whether the service is intended to inform a security review, support an investigation, or contribute to a broader assurance process. The brief should identify authorised information sources, permitted data categories, retention expectations, and exclusions such as private areas or unrelated activity. Avoid translating a client concern into an implied guarantee about detection, identification, coverage, or protection. A written boundary keeps procurement, privacy review, and later acceptance aligned with the question the project is actually allowed to answer.
CONTEXT & UNCERTAINTY / 02
Align stakeholders and protected services
Treat the site as an operating community with competing duties. Enterprise projects commonly involve security, facilities, safety, information governance, legal counsel, occupational representatives, and owners of protected or safety-critical services. An integrator should create a responsibility record showing who defines the concern, who authorises information use, who reviews findings, and who accepts residual uncertainty. Protected services deserve explicit consideration because monitoring changes may affect maintenance windows, electromagnetic compatibility work, access controls, or continuity plans. The design discussion should also document safe offsets from sensitive activities and any restrictions imposed by aviation, privacy, spectrum, or property rules. This is governance design, not a promise that technology will resolve every stakeholder risk.
PROTECTION & COMPLIANCE / 03
Govern interfaces, privacy, and EMC
Make integration boundaries visible before technical commitments are made. A defensible proposal describes interfaces by purpose and authority rather than exposing operational connection details. Document which systems may exchange approved status or case information, the owner of each interface, access approval, audit responsibility, data minimisation, and change control. Privacy review should address lawful basis, notice, retention, human review, and handling of incidental information. EMC and safety reviews should identify nearby protected services, test constraints, maintenance ownership, and escalation routes for interference concerns. Keep supplier-specific credentials, network endpoints, algorithms, thresholds, signal-control methods, and target-selection logic outside public guidance. The result is an integration contract that can be reviewed without turning it into an operating manual.
GOVERNANCE & VALIDATION / 04
Validate through the lifecycle
Acceptance should test documented assumptions, not advertise certainty. Validation is strongest when it follows the project lifecycle: requirements baseline, design review, controlled commissioning, operational governance review, and periodic reassessment. Each stage should preserve the authorised information inputs, known limitations, privacy decisions, EMC findings, human-review responsibilities, and records of changes. Written validation can confirm that the service behaves within its approved scope and that uncertainty is visible to decision-makers; it should not claim universal performance or guaranteed site protection. Revisit the boundary when buildings, tenants, protected services, legal permissions, or threat concerns change. Integrators can then provide an auditable decision trail rather than a static equipment handover.
TECHNICAL & COMPLIANCE BOUNDARY / 05
This guide is an educational project reference—not an operating, deployment, integration, or performance instruction.
01Availability and interpretation of acoustic, RF, radar, EO/IR, visual, and other information depend on site conditions, environment, data quality, protected services, permissions, privacy, and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, availability, safety, non-interference, or risk outcomes.
02Any equipment, interface, data handling, industrial-system connection, spectrum-related arrangement, aviation coordination, or later project decision requires appropriate authority, engineering review, qualified personnel, and written scope.
03The public guide does not provide target selection, sensor positioning, thresholds, algorithms, execution sequences, signal control, interference, navigation manipulation, or response methods.
BLOG FAQ / 404
Frequently asked questions on Enterprise UAV Detection: Integrator Project Context.
These answers support bounded, project-level discussion. They are not an operating, deployment, integration, or field-outcome instruction.
RECORDTECHNICAL LIBRARY / GOVERNED INFORMATION FAQ
NEXT STEP / PROJECT PATH
Discuss PCBA delivery and custom-project conditions.
From sensing modules to system integration, interfaces, environmental fit, certification, and documentation scope belong in a written project definition.
CONTINUE THE READING
CONTENT DISTRIBUTION / SHARE
Share this reviewed project release.
Opens the platform share interface in a new window.
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
How Acoustic Sensors Add Detection Capability for Modern FPV UAVs
How Acoustic Sensors Add Detection Capability for Modern FPV UAVs should be discussed as a bounded project question about acoustic information in modern FPV contexts, not as a promise that a technology will detect, identify, locate, track, cover, or protect a particular site. A responsible C-UAS review starts with authority, protected services, privacy, safety, environmental context, accountable human review, and written validation before it treats any sensor indication as decision-ready evidence.
Building a Detection Layer for Drones With Limited RF Activity
Building a Detection Layer for Drones With Limited RF Activity should be discussed as a bounded project question about a bounded information layer for limited-RF context, not as a promise that a technology will detect, identify, locate, track, cover, or protect a particular site. A responsible C-UAS review starts with authority, protected services, privacy, safety, environmental context, accountable human review, and written validation before it treats any sensor indication as decision-ready evidence.