BLOG / TECHNICAL LIBRARY 431
Acoustic Sensors as a Governed Detection Upgrade for Existing Security Networks
Adding passive acoustic sensing to an established security network is a project-governance question, not a promise of detection. This guide helps public sites examine whether an acoustic input can be authorised, privacy-bounded, technically integrated, and independently validated alongside existing security information—without prescribing placement, coverage, thresholds, or response actions.
INFORMATION & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put technology questions back into an authorised, reviewable, and verifiable project context.
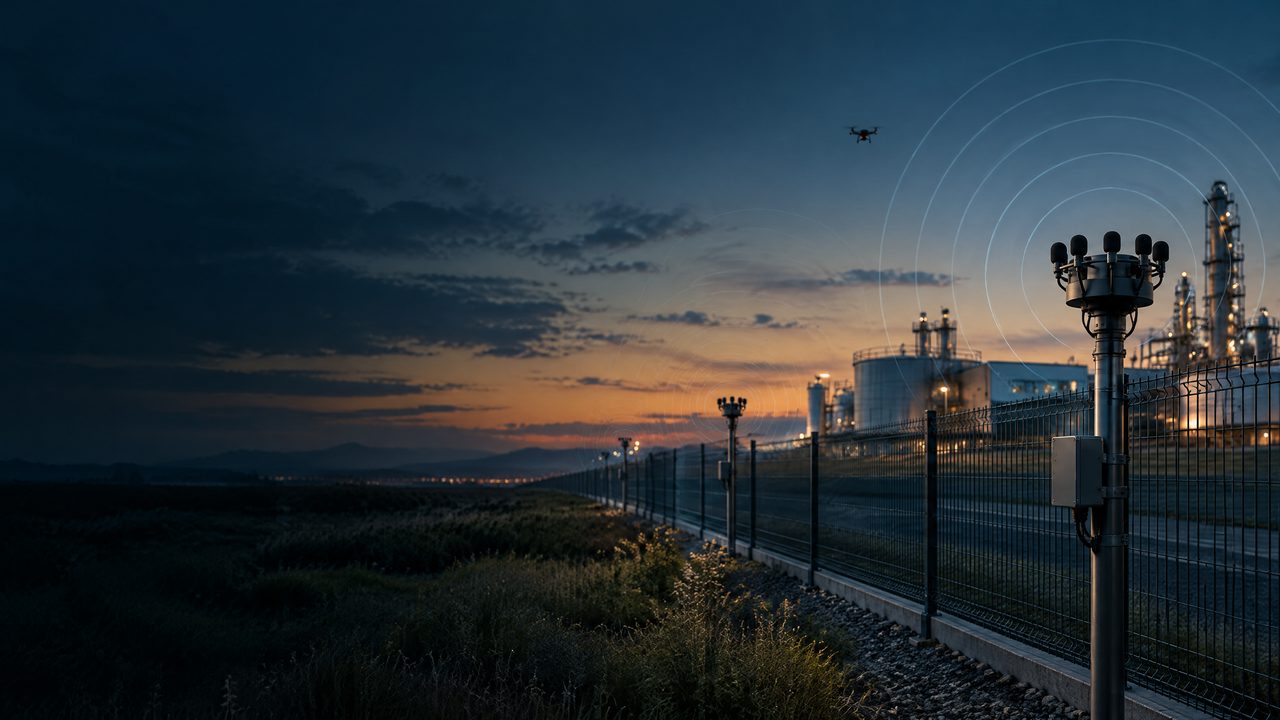
This conceptual scene helps explain conditional information, protected services, human review, and written validation. It is not a deployment or field-outcome claim.
BLOG SUMMARY
Upgrade the evidence chain, not the authority to act
A responsible acoustic-sensing project starts with a documented purpose, protected-service constraints, and a clear boundary between observation and intervention. Define what the network may record, who may review it, how human accountability is maintained, and what written evidence is required before any operational reliance. Treat acoustic data as one contextual input among others, with uncertainty and limitations visible to decision-makers.
TERMS IN THIS GUIDE
Hover, focus, or tap a term for a bounded definition. Each definition links to the terminology reference.
PROJECT QUESTION / 01
1. Frame the upgrade around an authorised public purpose
Document the safety, security, or continuity objective in plain language and identify the authority responsible for approving it. Separate a legitimate monitoring purpose from any wish to identify or act against a particular aircraft. Record protected services, public access, emergency operations, and aviation responsibilities that must remain undisturbed. The project brief should state what is out of scope—including intervention, radio control, interference, navigation manipulation, and target selection—so procurement and review cannot silently expand the mandate.
CONTEXT & UNCERTAINTY / 02
2. Set a privacy and data boundary before technical design
Acoustic collection may intersect with conversations, bystanders, workers, neighbouring properties, or other sensitive sound sources. Establish minimisation, retention, access, audit, deletion, and disclosure rules with the relevant privacy and legal owners before asking what the system might classify. Require accountable human review for consequential interpretation, and define how uncertainty, false alerts, inaccessible evidence, and requests from protected services are documented. A privacy impact assessment and records-of-processing style register can make the boundary testable without prescribing sensor layout or analytic methods.
PROTECTION & COMPLIANCE / 03
3. Treat integration as an assurance case
Evaluate the proposed input at the interface level: data ownership, time synchronisation, identity and access control, logging, cybersecurity, fail-safe behaviour, maintenance responsibility, and the meaning of an alert in existing records. Consider EMC and radio-compliance obligations, aviation and site rules, accessibility, weather and environmental effects, and dependencies on protected communications or life-safety systems. Any assertion about suitability, accuracy, identification, coverage, or a particular UAV or location must be supported by written validation under an approved test plan—not by a manufacturer claim or an unreviewed demonstration.
GOVERNANCE & VALIDATION / 04
4. Make acceptance conditional, reversible, and reviewable
Use a staged, documented decision gate: approved requirements; privacy, safety, aviation, and compliance review; controlled evidence collection; independent assessment; human-factors review; and a signed acceptance record. Define stop, pause, rollback, and re-authorisation criteria at the project level, including loss of data integrity, unexpected privacy impact, EMC concerns, or conflict with protected services. Publish the limits of the evidence to stakeholders, revisit them after material system or site changes, and never convert an experimental acoustic feed into operational reliance without renewed written validation.
TECHNICAL & COMPLIANCE BOUNDARY / 05
This guide is an educational project reference—not an operating, deployment, integration, or performance instruction.
01Availability and interpretation of acoustic, RF, radar, EO/IR, visual, and other information depend on site conditions, environment, data quality, protected services, permissions, privacy, and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, availability, safety, non-interference, or risk outcomes.
02Any equipment, interface, data handling, industrial-system connection, spectrum-related arrangement, aviation coordination, or later project decision requires appropriate authority, engineering review, qualified personnel, and written scope.
03The public guide does not provide target selection, sensor positioning, thresholds, algorithms, execution sequences, signal control, interference, navigation manipulation, or response methods.
BLOG FAQ / 431
Frequently asked questions on Acoustic Sensors as a Governed Detection Upgrade for Existing Security Networks.
These answers support bounded, project-level discussion. They are not an operating, deployment, integration, or field-outcome instruction.
RECORDTECHNICAL LIBRARY / GOVERNED INFORMATION FAQ
NEXT STEP / PROJECT PATH
Discuss PCBA delivery and custom-project conditions.
From sensing modules to system integration, interfaces, environmental fit, certification, and documentation scope belong in a written project definition.
CONTINUE THE READING
CONTENT DISTRIBUTION / SHARE
Share this reviewed project release.
Opens the platform share interface in a new window.
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
Acoustic Drone Detection vs. RF Detection: Why Critical Infrastructure Needs Multiple Sensors
A governance-first comparison of passive acoustic and RF information roles for airports, energy facilities, ports, data centres and other critical infrastructure. It explains conditional evidence, protected services, accountable review, lawful authority, integration and written validation—not a sensor prescription, placement plan, threshold, signal-control method or performance claim.
Drone Detection for Critical Infrastructure: A Project Guide for Airports, Energy Facilities and Data Centers
A governance-first guide to discussing acoustic, RF, radar, EO/IR and visual information for airports, energy facilities, ports and data centres. It frames protected services, conditional evidence, interfaces and written validation—not a sensor prescription, deployment plan, threshold, control method or performance claim.