BLOG / TECHNICAL LIBRARY 156
How Should Industry Assess Acoustic UAV Detection for Perimeter Security?
For an industrial operator, the project question is not whether acoustic sensing can promise a complete counter-UAS answer. It is how an authorised team can assess where acoustic information may add context to perimeter security while protecting people, production, privacy, and lawful operations. This guide frames discovery around defined information inputs, protected services, safety offsets, human review, and written validation. Acoustic, RF, radar, EO/IR, and fusion are treated as conditional and complementary contexts—not guaranteed capabilities—and no intervention or signal-control method is described.
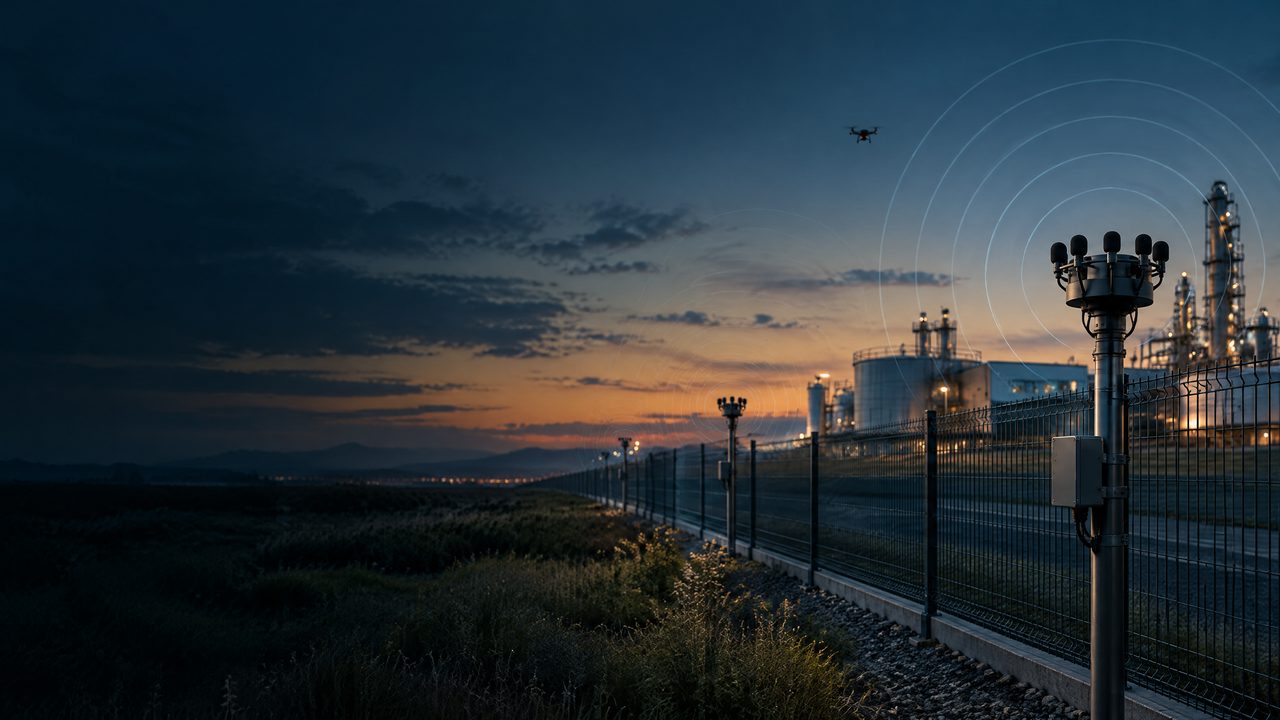
INFORMATION & PROJECT-GOVERNANCE CONTEXT / CONCEPTUAL SCENE
Put technology questions back into an authorised, reviewable, and verifiable project context.
This conceptual scene helps explain conditional information, protected services, human review, and written validation. It is not a deployment or field-outcome claim.
BLOG SUMMARY
A defensible project question
The right starting point is a written assessment of the security outcome, the protected industrial services, and the authorised information the project may use. Acoustic detection can be considered as one contextual input alongside RF, radar, EO/IR, or fusion, subject to environment, governance, and validation. Any design must preserve safety offsets, privacy and spectrum/legal considerations, human review, and documented acceptance criteria before it is relied upon.
TERMS IN THIS GUIDE
Hover, focus, or tap a term for a bounded definition. Each definition links to the terminology reference.
INFORMATION CONTEXT / 01
Define the perimeter question
Begin by stating what the industrial site needs to understand, rather than assuming a particular sensor or outcome. Describe the protected services, safety-critical areas, operating constraints, and authorised information sources in writing. The assessment should distinguish awareness from decision-making and should identify where false context, missing context, or delayed context could affect people or continuity. Acoustic information may be relevant in some conditions, but it should be evaluated as a conditional input, not presented as a universal detection promise or a substitute for accountable security governance. Keep the question narrow enough to validate and clear enough for every stakeholder to interpret consistently.
CONDITIONS & UNCERTAINTY / 02
Treat modalities as complementary context
A credible review compares acoustic information with other authorised contexts such as RF, radar, EO/IR, or a fusion layer without assuming that any one source is complete. The comparison should remain project-specific and non-operational: document environmental uncertainty, data rights, interoperability needs, and the limits of interpretation. Do not infer performance, coverage, target selection, or response capability from the presence of a modality. The useful deliverable is a bounded evidence model that shows what can be reviewed and what must remain unconfirmed. It should also state which claims require further written validation before they can influence a protected service.
CORROBORATION / 03
Build safety and compliance boundaries
The project must preserve explicit safety offsets around people, protected services, and safety-critical operations, with human review before any security conclusion is accepted. Privacy obligations, lawful spectrum use, site rules, procurement controls, and other applicable legal considerations should be assessed by the authorised owners. Inputs must be collected and handled only under approved permissions, retention rules, and access controls. No design assumption should enable jamming, navigation manipulation, evasion, or an intervention workflow; the boundary is information support under accountable oversight. The same boundary should be visible in requirements, supplier discussions, governance records, and acceptance documents.
GOVERNANCE & VALIDATION / 04
Validate in writing before reliance
Close the discovery phase with written validation agreed by security, operations, safety, privacy, legal, and system-integration stakeholders. Record the question being tested, authorised inputs, protected services, safety offsets, review responsibilities, known limitations, and conditions under which evidence is insufficient. Acceptance should be based on documented project evidence rather than generic claims, and any change in site context or data authority should trigger renewed review. This creates a defensible basis for deciding whether acoustic context belongs in the wider security architecture at all. The record should preserve dissent, unresolved uncertainty, and ownership for future review rather than implying certainty.
TECHNICAL & COMPLIANCE BOUNDARY / 05
This guide is an educational project reference—not an operating, deployment, integration, or performance instruction.
01Availability and interpretation of acoustic, RF, radar, EO/IR, visual, and other information depend on site conditions, environment, data quality, protected services, permissions, privacy, and accountable review. This page does not promise detection, identification, classification, location assessment, tracking, availability, safety, non-interference, or risk outcomes.
02Any equipment, interface, data handling, industrial-system connection, spectrum-related arrangement, aviation coordination, or later project decision requires appropriate authority, engineering review, qualified personnel, and written scope.
03The public guide does not provide target selection, sensor positioning, thresholds, algorithms, execution sequences, signal control, interference, navigation manipulation, or response methods.
BLOG FAQ / 156
Frequently asked questions on How Should Industry Assess Acoustic UAV Detection for Perimeter Security?.
These answers support bounded, project-level discussion. They are not an operating, deployment, integration, or field-outcome instruction.
RECORDTECHNICAL LIBRARY / GOVERNED INFORMATION FAQ
NEXT STEP / PROJECT PATH
Discuss PCBA delivery and custom-project conditions.
From sensing modules to system integration, interfaces, environmental fit, certification, and documentation scope belong in a written project definition.
CONTINUE THE READING
CONTENT DISTRIBUTION / SHARE
Share this reviewed project release.
Opens the platform share interface in a new window.
Review the full ARC-PERIMETER perimeter solution.
A consolidated reference from microphone-array networking to layered perimeters and project validation.
Acoustic Drone Detection vs. RF Detection: Why Critical Infrastructure Needs Multiple Sensors
A governance-first comparison of passive acoustic and RF information roles for airports, energy facilities, ports, data centres and other critical infrastructure. It explains conditional evidence, protected services, accountable review, lawful authority, integration and written validation—not a sensor prescription, placement plan, threshold, signal-control method or performance claim.
Drone Detection for Critical Infrastructure: A Project Guide for Airports, Energy Facilities and Data Centers
A governance-first guide to discussing acoustic, RF, radar, EO/IR and visual information for airports, energy facilities, ports and data centres. It frames protected services, conditional evidence, interfaces and written validation—not a sensor prescription, deployment plan, threshold, control method or performance claim.